Skip to content
Zaun Ember

Security operations, connected.

Ember by Zaun connects telemetry, detection, investigation, and response. Keep the evidence visible and define where automation can act across your environment.

ConnectBring available telemetry together
InvestigateReview the supporting evidence
RespondAct through agreed permissions
ReviewKeep coverage and limits visible
Why now

More automated activity. More to understand.

Agents add activity across identity, cloud, developer tools, and endpoints. Understanding that activity means connecting events to the people, systems, and authority behind them.

Ember brings those signals into detection and investigation workflows. Your team reviews the evidence and decides which response actions can run automatically.

Signal volumeidentity · cloud · endpoint · networkhuman alertsagent incidents

Illustrative activity stream. The event counts compare a sample user and agent scenario; they are not customer measurements.

Security Programs

Build the security program your work needs.

Connect identity, endpoint, cloud, and insider risk workflows to the sources your organization uses. Review the available evidence, response permissions, and rollout requirements with our engineers.
IdentityIdentity Threat Detection and Response (ITDR)Investigate suspicious account behavior across connected identity providers.
EndpointManaged Endpoint Detection and Response (MEDR)Detection and response workflows built around your connected endpoint tools.
CloudCloud Security Beyond Posture (CDR)Posture and runtime in one investigation queue, across AWS, Azure, and GCP.
InsiderInsider Threat ProgramBehavioral baselines and audit-ready evidence, surfaced above the noise.
Powered by
AWS
AWS
Azure
Azure
GCP
GCP
Lumen
Lumen
ClickHouse
ClickHouse
Cerebras
Cerebras
Anthropic
Anthropic
OpenAI
OpenAI
Connection

Start with the systems you use.

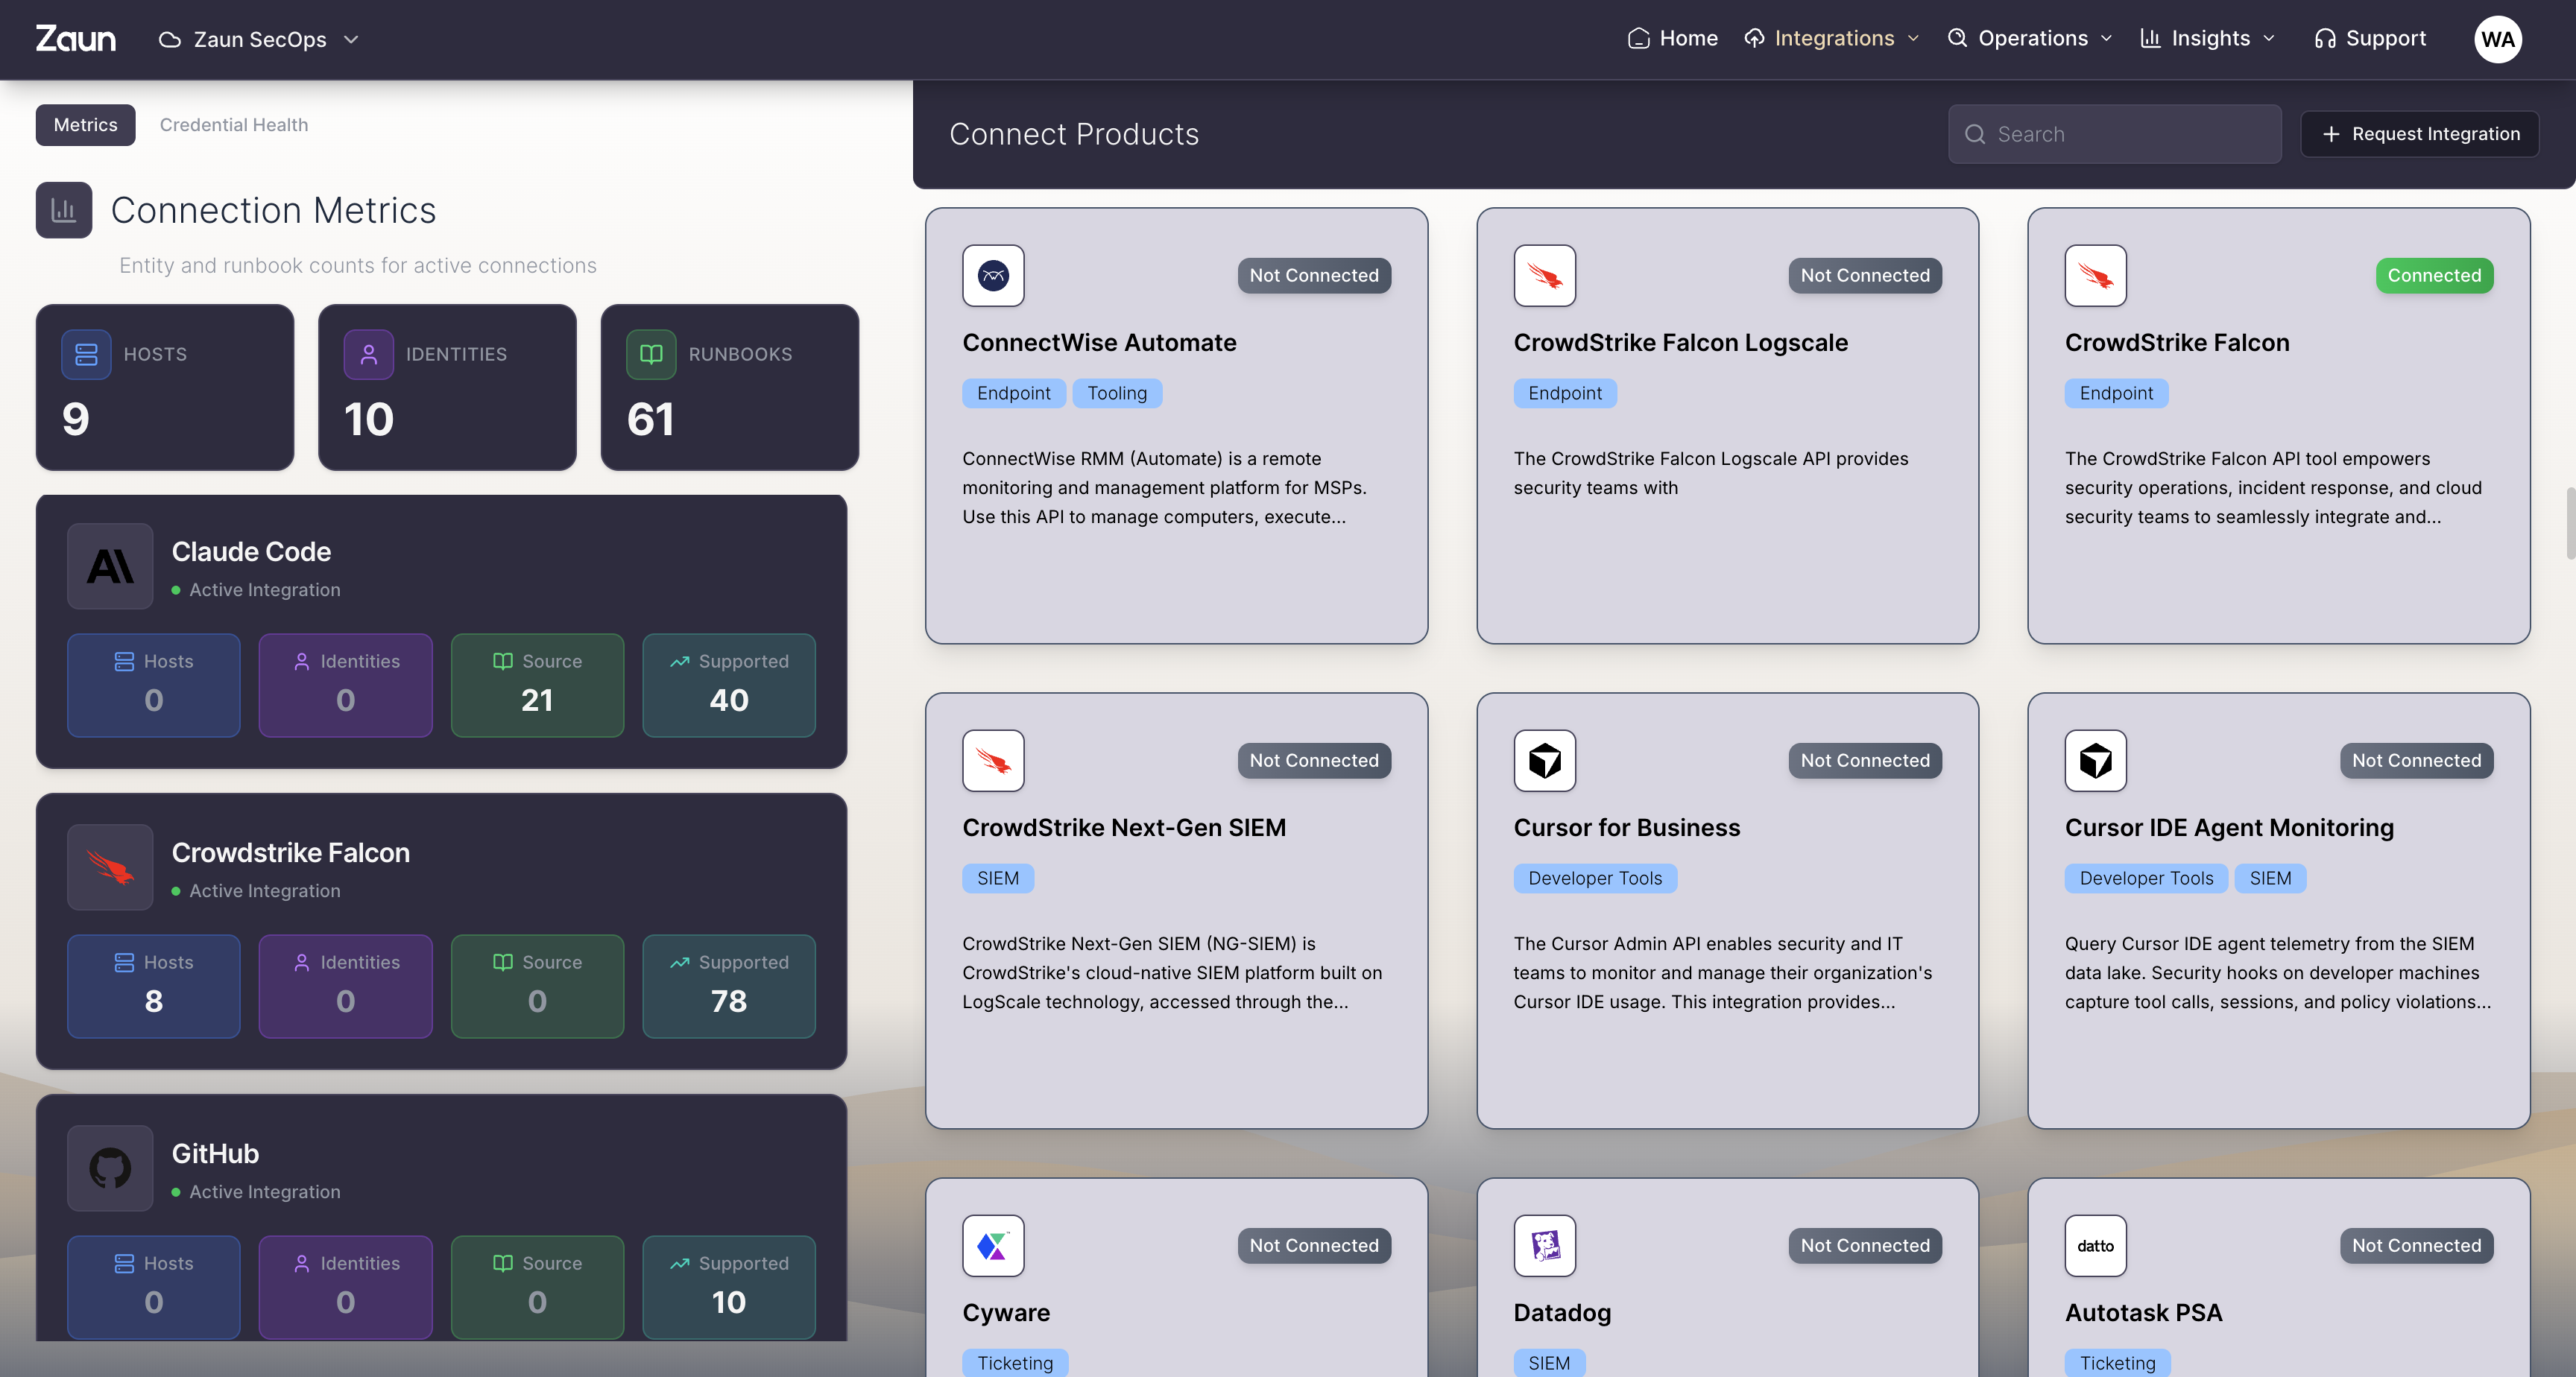
Connect supported cloud, identity, endpoint, SaaS, and AI sources. Review the credentials, telemetry, and permissions each integration provides before enabling the workflow.
Sources
defined coverage
OAuth
first auth
Review
connection health
Product view / integrations directory
Zaun integrations directory with connection metrics and connect products
Zaun

Diagrams and sample records illustrate the workflow. Product views are identified separately; example metrics are not customer results.

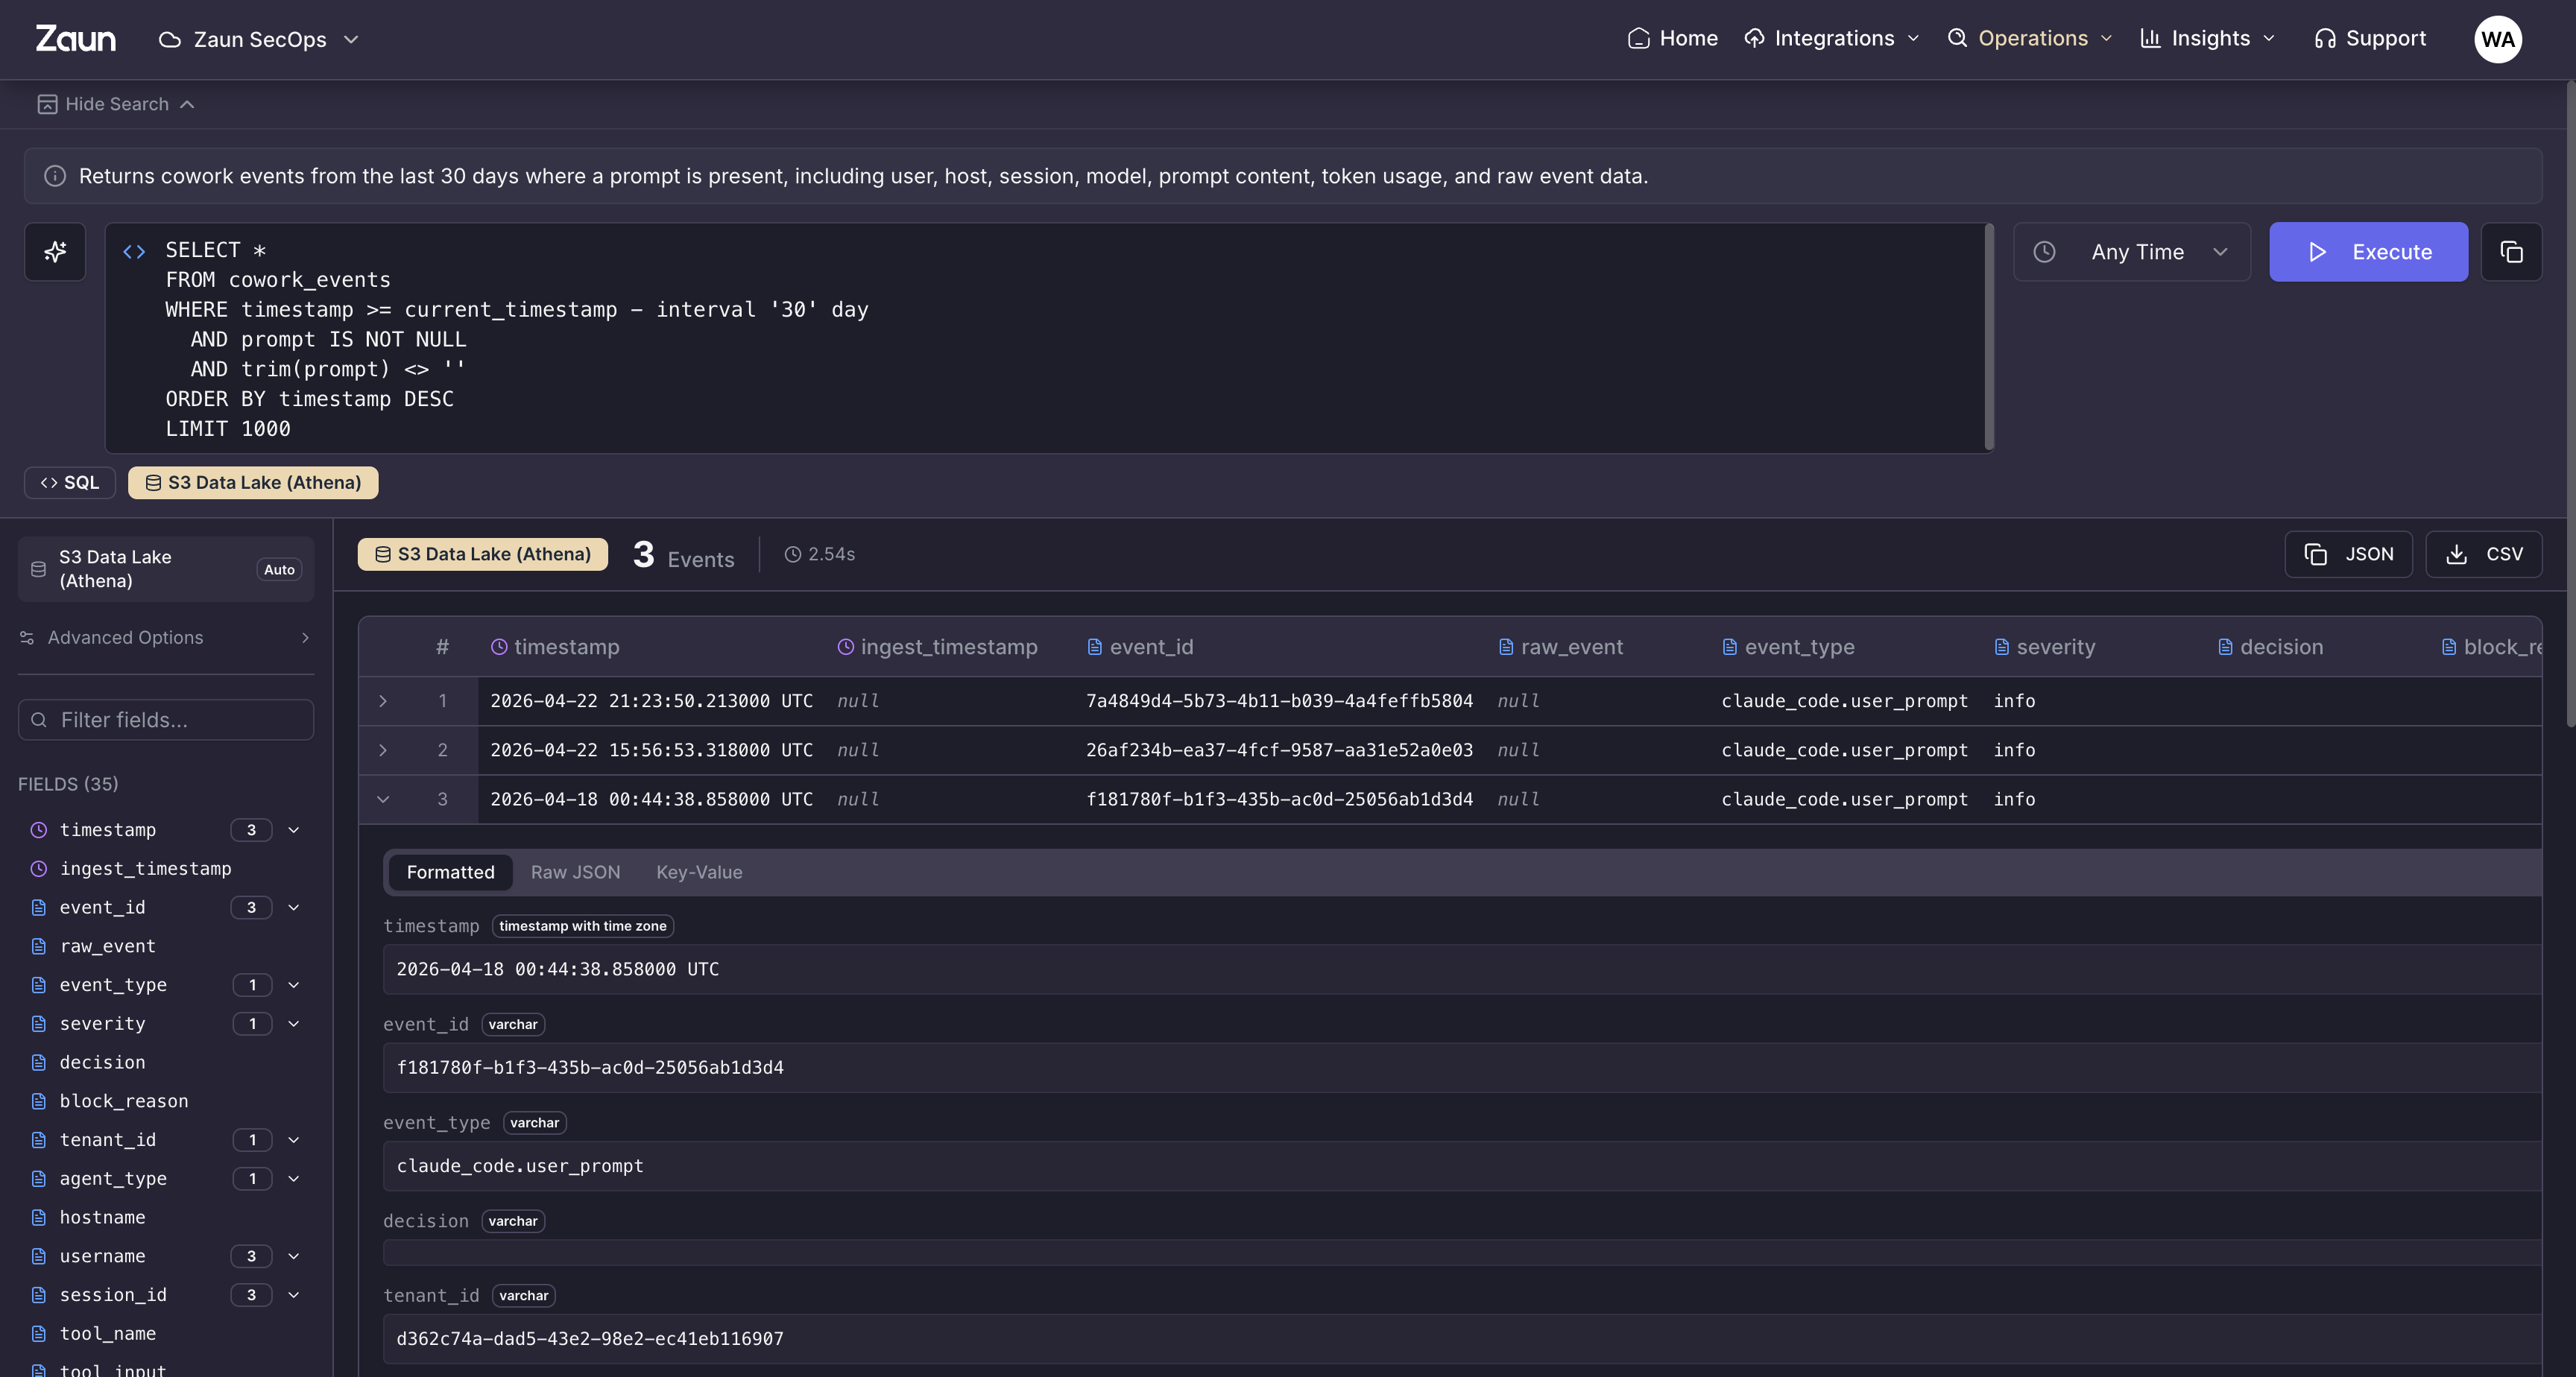
Zaun Lake

Deep retention. Real hunts.

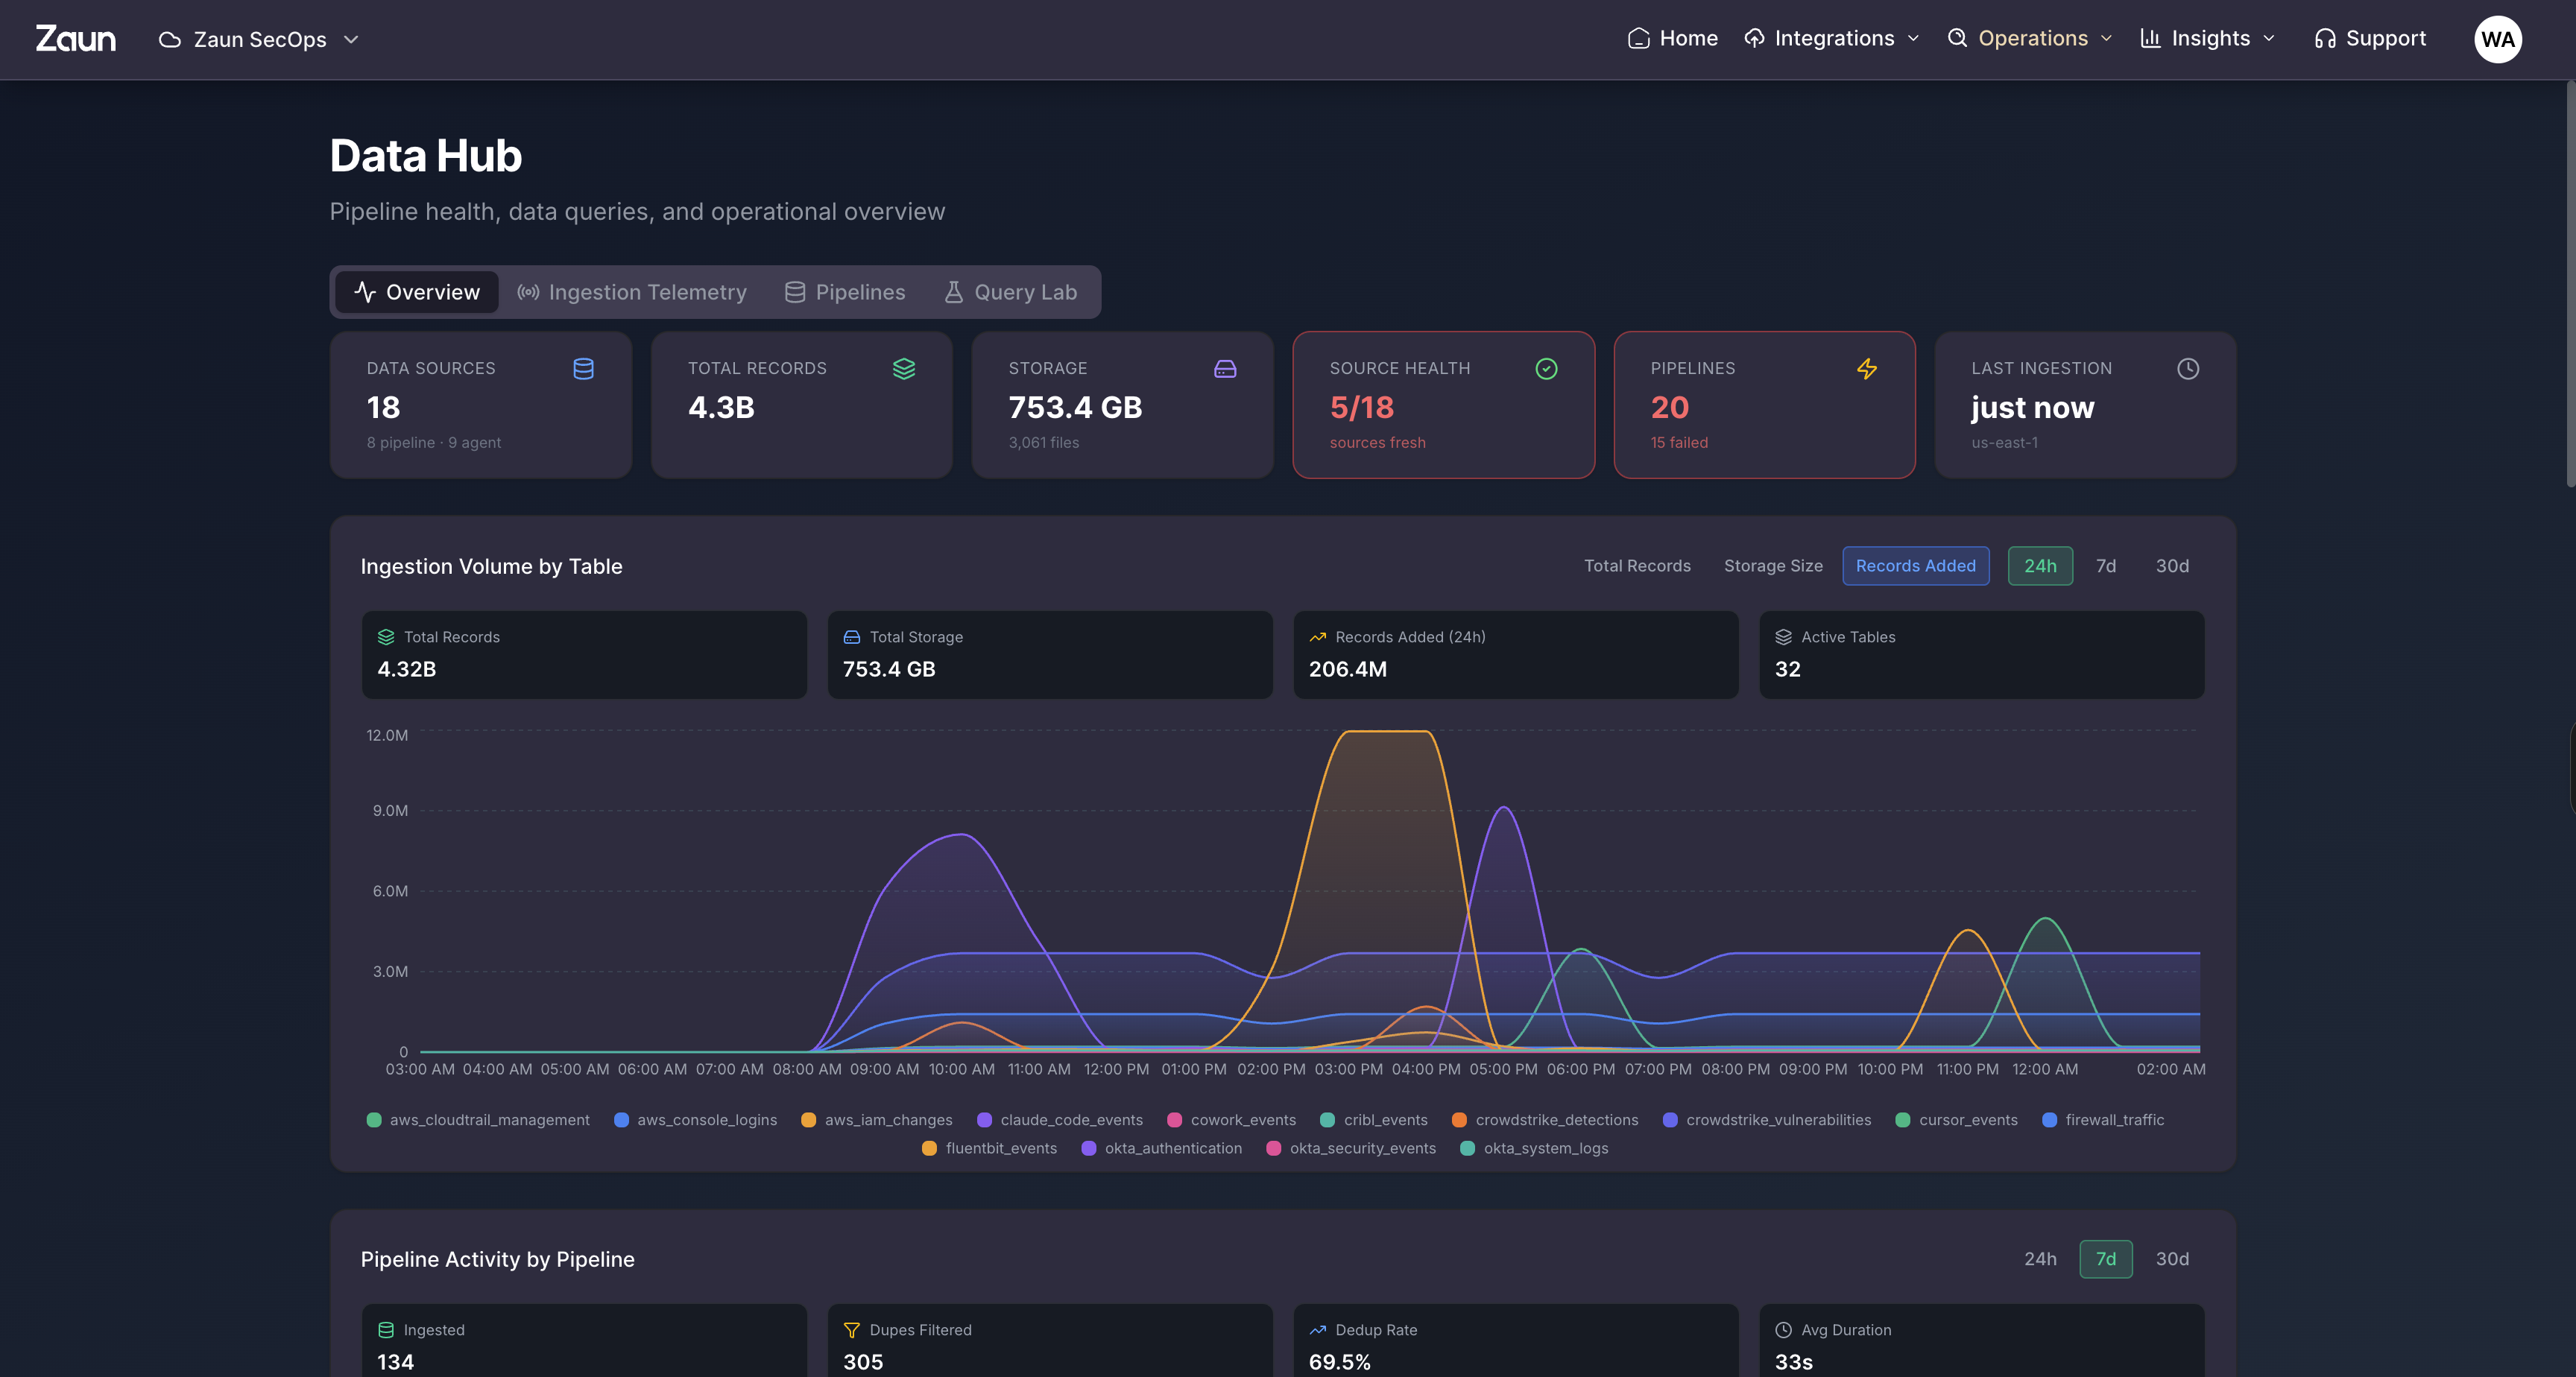
Zaun Lake brings supported telemetry into a searchable record for investigation and review. Connect available authentication, sensitive action, configuration, and other security events. Review collection, retention, query support, and evidence mappings for the sources your organization uses.

Powered by
Fluent BitAWS AthenaClickHouse
Tagging · live
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
PCI.10
· drop
API
NIST.AU
GET
SAML
HIPAA.A
CMD
· drop
AUTH
NIST.AC
· drop
OAUTH
· drop
NIST.IA
4xx
IDP
SOC2.CC
· drop
EDR
PCI.10
· drop
API
NIST.AU
⌁ zaun lakesample retained 1.4% · dropped 98.6%
Product view / zaun lake explorer
Zaun Lake data hub with ingestion telemetry and pipeline activity
Product view / zaun lake explorer
Zaun Lake data hub with ingestion telemetry and pipeline activity
CollectSupported source events
RetainConfigured policies
InvestigateConnected telemetry
ReviewAvailable evidence

Diagrams and sample records illustrate the workflow. Product views are identified separately; example metrics are not customer results.

Detection & Runbooks

Detections you can read out loud.

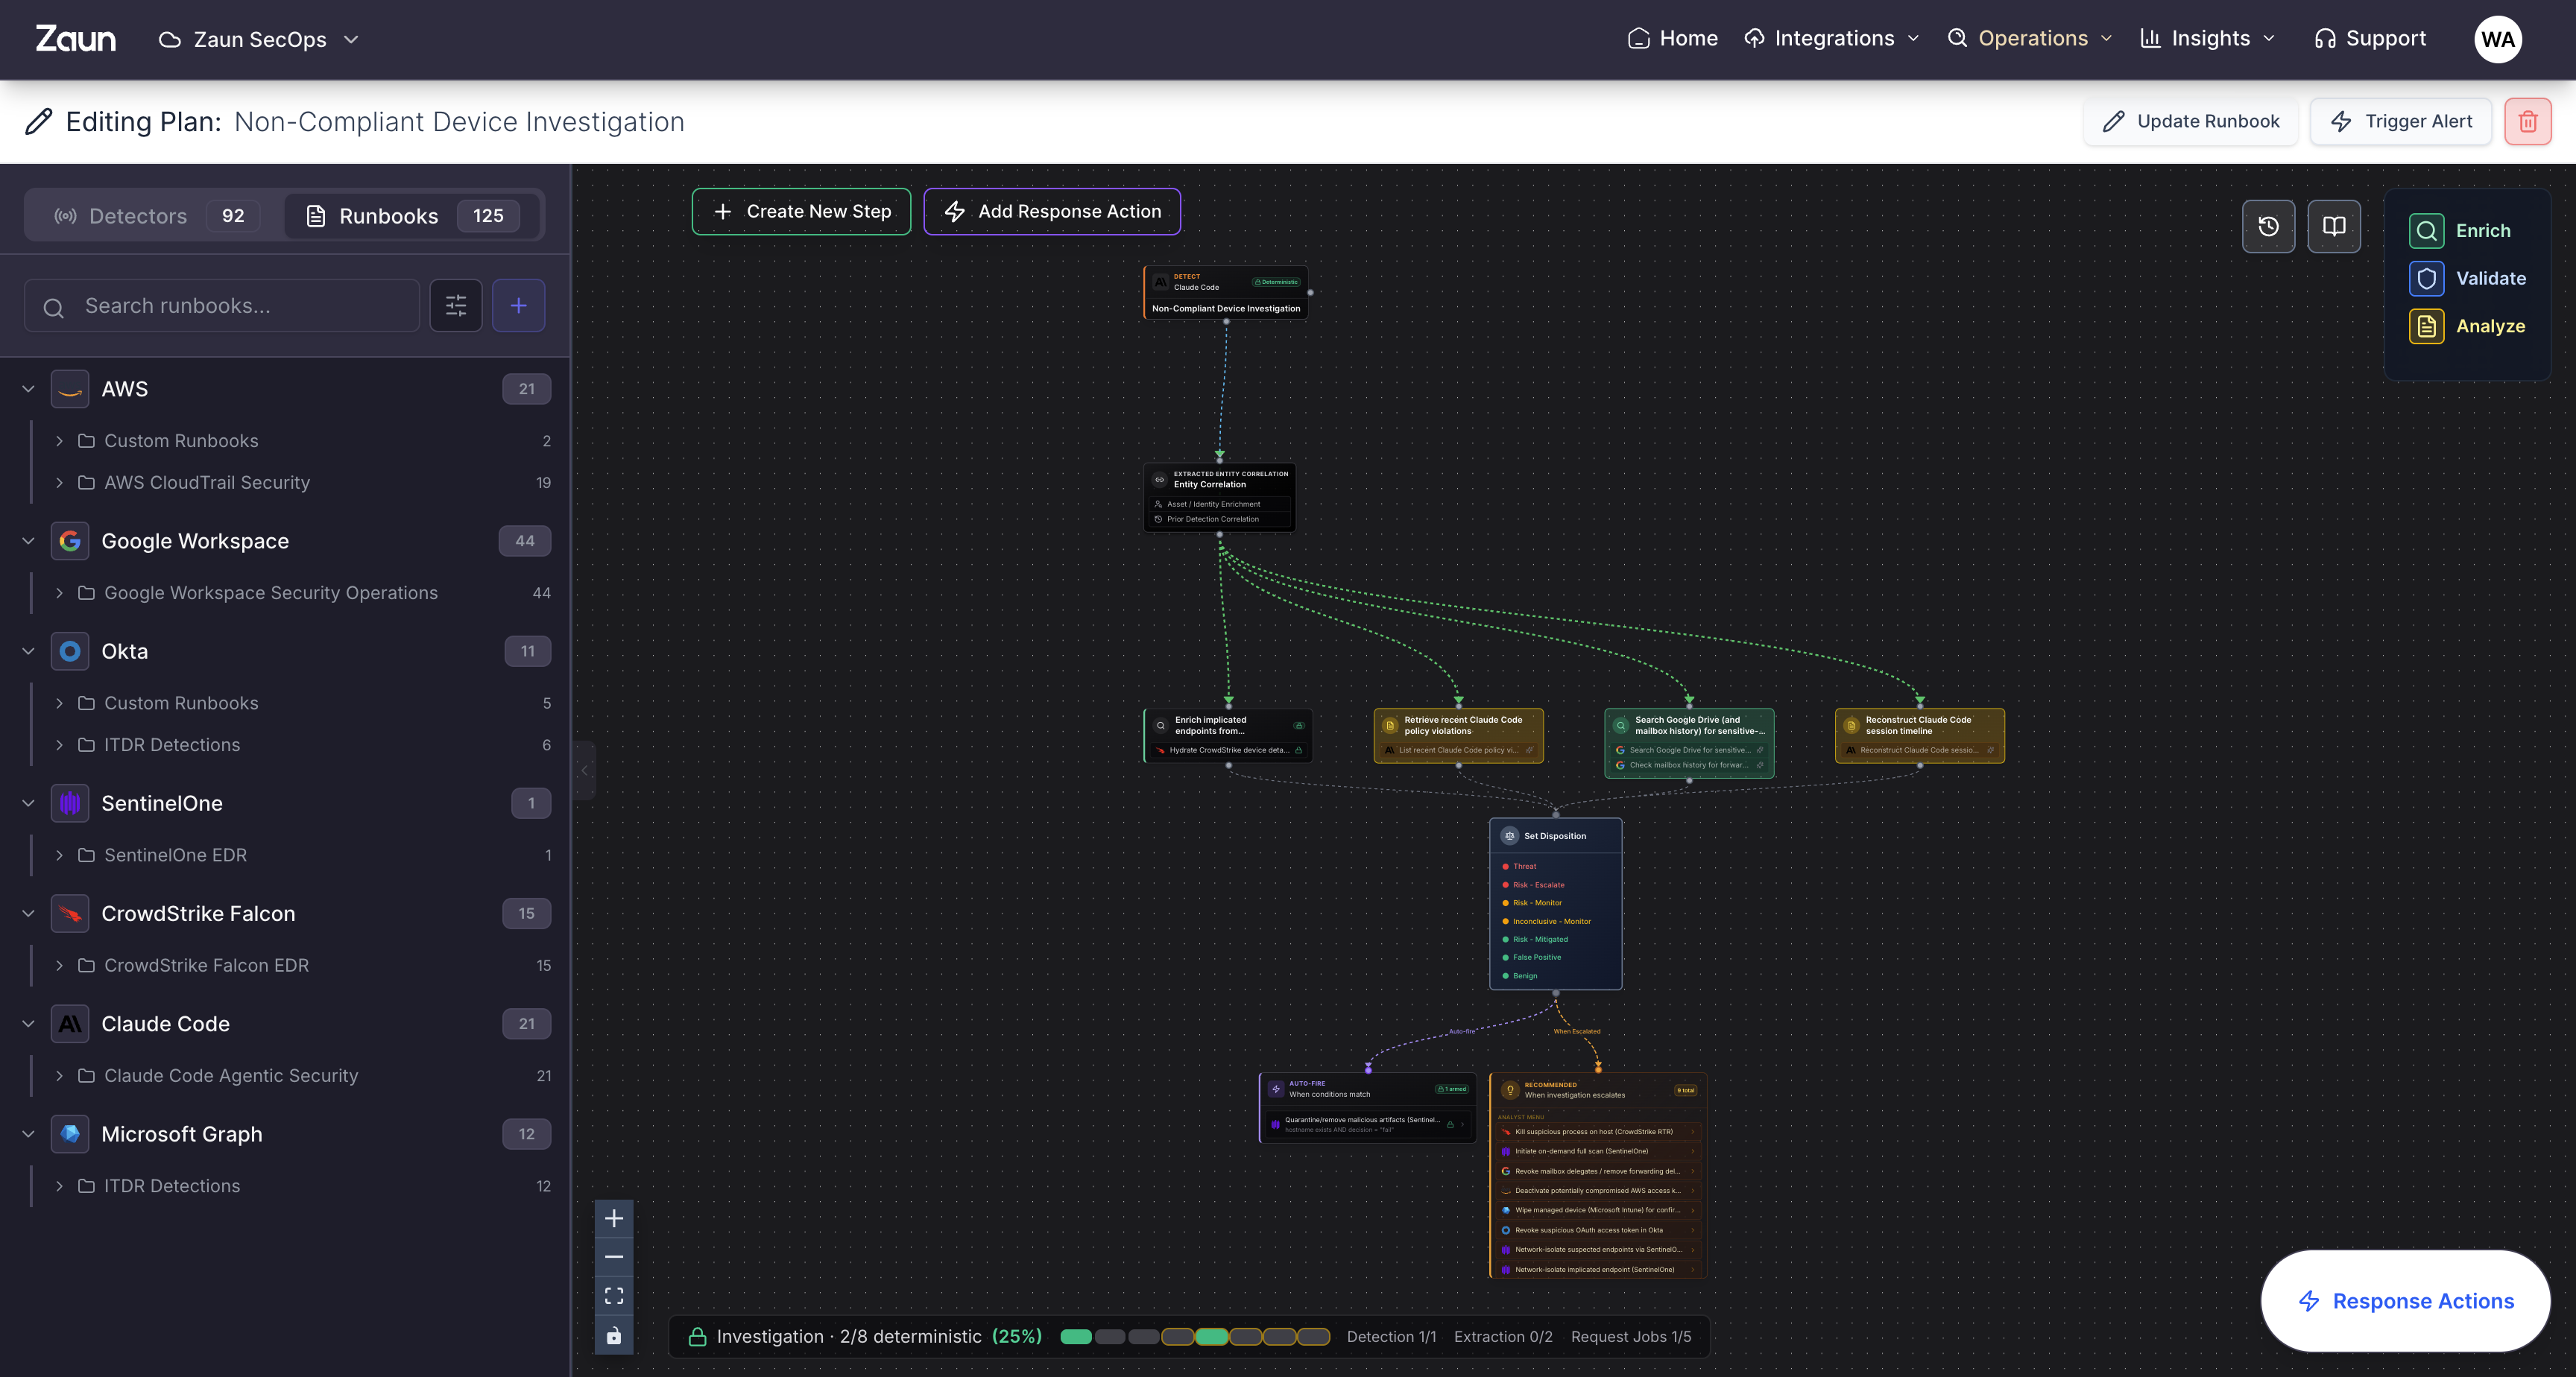
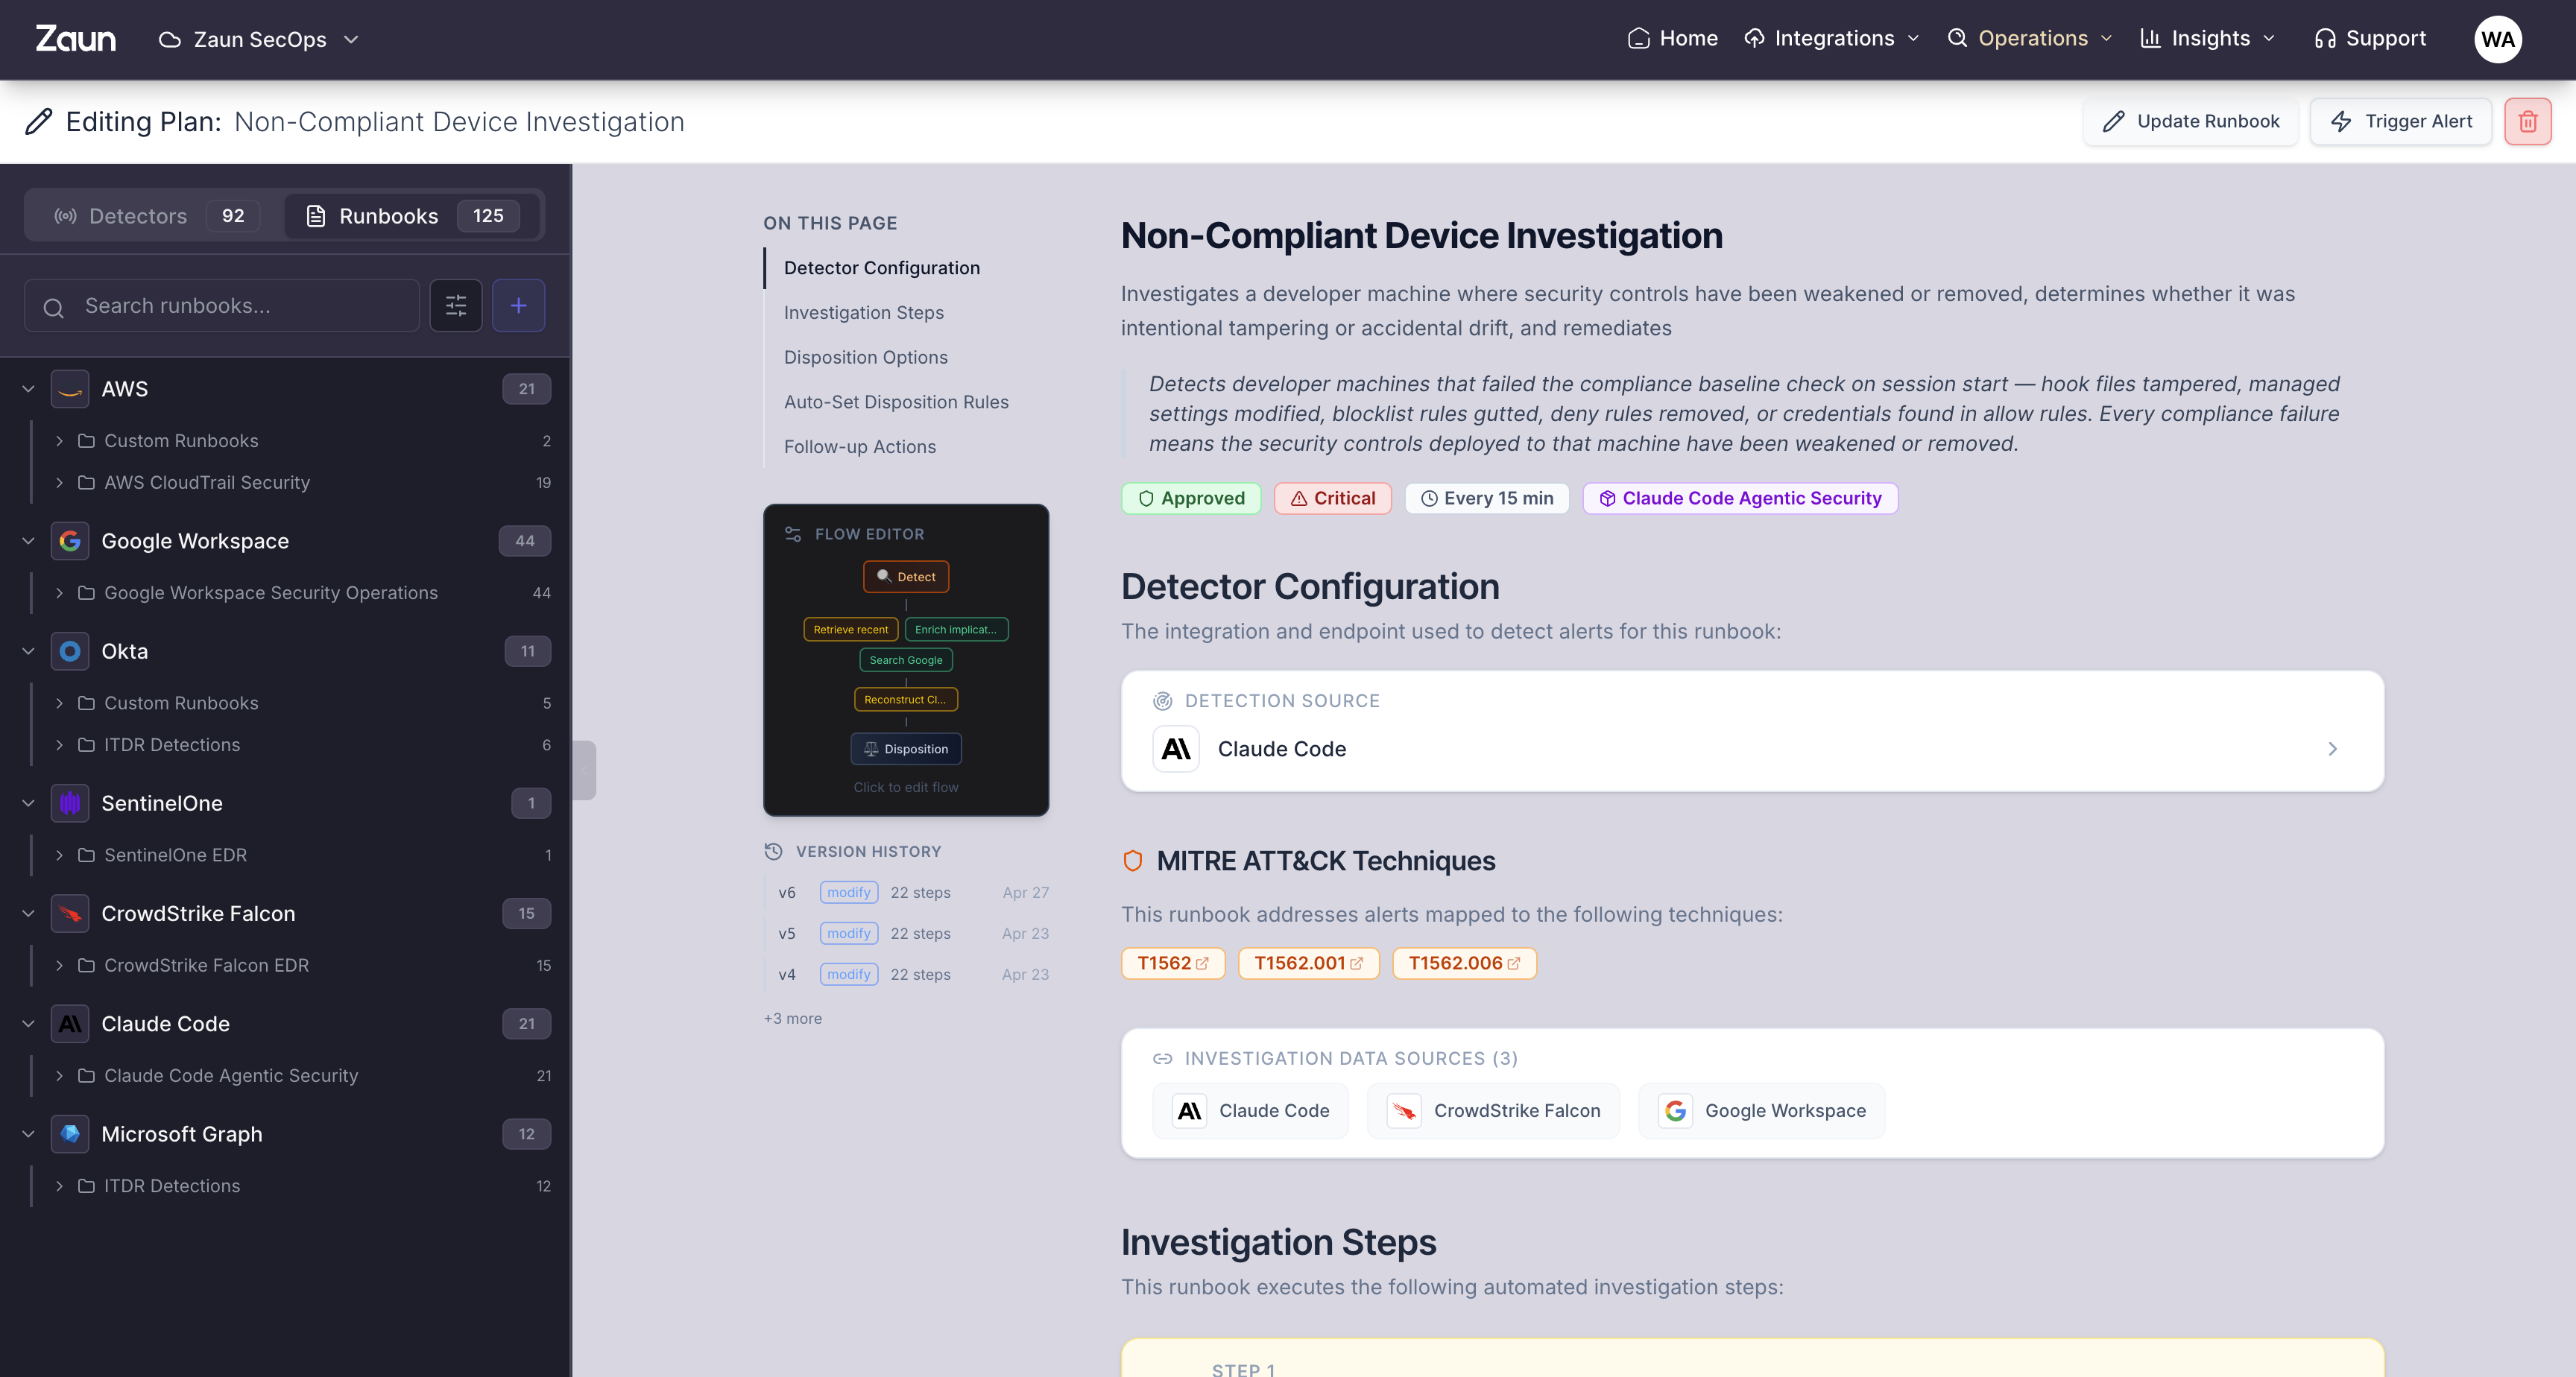
Review detections and runbooks with their technique mappings, evidence, and response steps. MITRE ATT&CK and D3FEND provide reference frameworks. Define which deterministic actions may run automatically and where an expert must review the recommendation.
Built on
MITRE ATT&CKtechnique IDsMITRE D3FENDcountermeasures
runbooks/oauth_grant_suspicious.zaun● modified
detection oauth_grant.suspicious
  mitre.attack  T1078.004
  mitre.defend  D3-LSAA

  when an OAuth grant is approved
   and scope is "drive.read" or "mail.read"
   and actor is in group "executive"
  then
   pause the grant
   open investigation "credential.exposure"
   ask actor in slack to confirm
   if no confirm in 30m: revoke and notify ciso

severity high
owner    identity
line 12, col 18compiled · 0 errors
Live · last 5firing
oauth_grant.suspicious
via okta·ATT&CK T1078.004
highnow
edr.process.unsigned_dll
via crowdstrike·ATT&CK T1574.002
med12s
iam.role.privilege_escalation
via aws·ATT&CK T1098.003
high47s
agent.tool.unapproved
via openai·ATT&CK T1059
low1m
auth.impossible_travel
via okta·ATT&CK T1078
med2m
Product view / runbook plan
Zaun runbook plan editor for Non-Compliant Device Investigation with detection, entity correlation, enrichment steps, and response actions
Product view / runbook plan
Zaun runbook plan editor for Non-Compliant Device Investigation with detection, entity correlation, enrichment steps, and response actions

Readable logic

Inspect the rule, its context, and the response workflow with your team.

Review and tune

Use findings, changes in the environment, and reviewer feedback to improve coverage.

Versioned and Auditable

Each rule and step is a Zaun artifact, version-controlled, and observable end to end.

Diagrams and sample records illustrate the workflow. Product views are identified separately; example metrics are not customer results.

Investigation

Investigations that show their work.

Bring evidence from available connected sources into a timeline and an investigation narrative. Review the finding, its supporting records, and recommended actions before granting response authority.
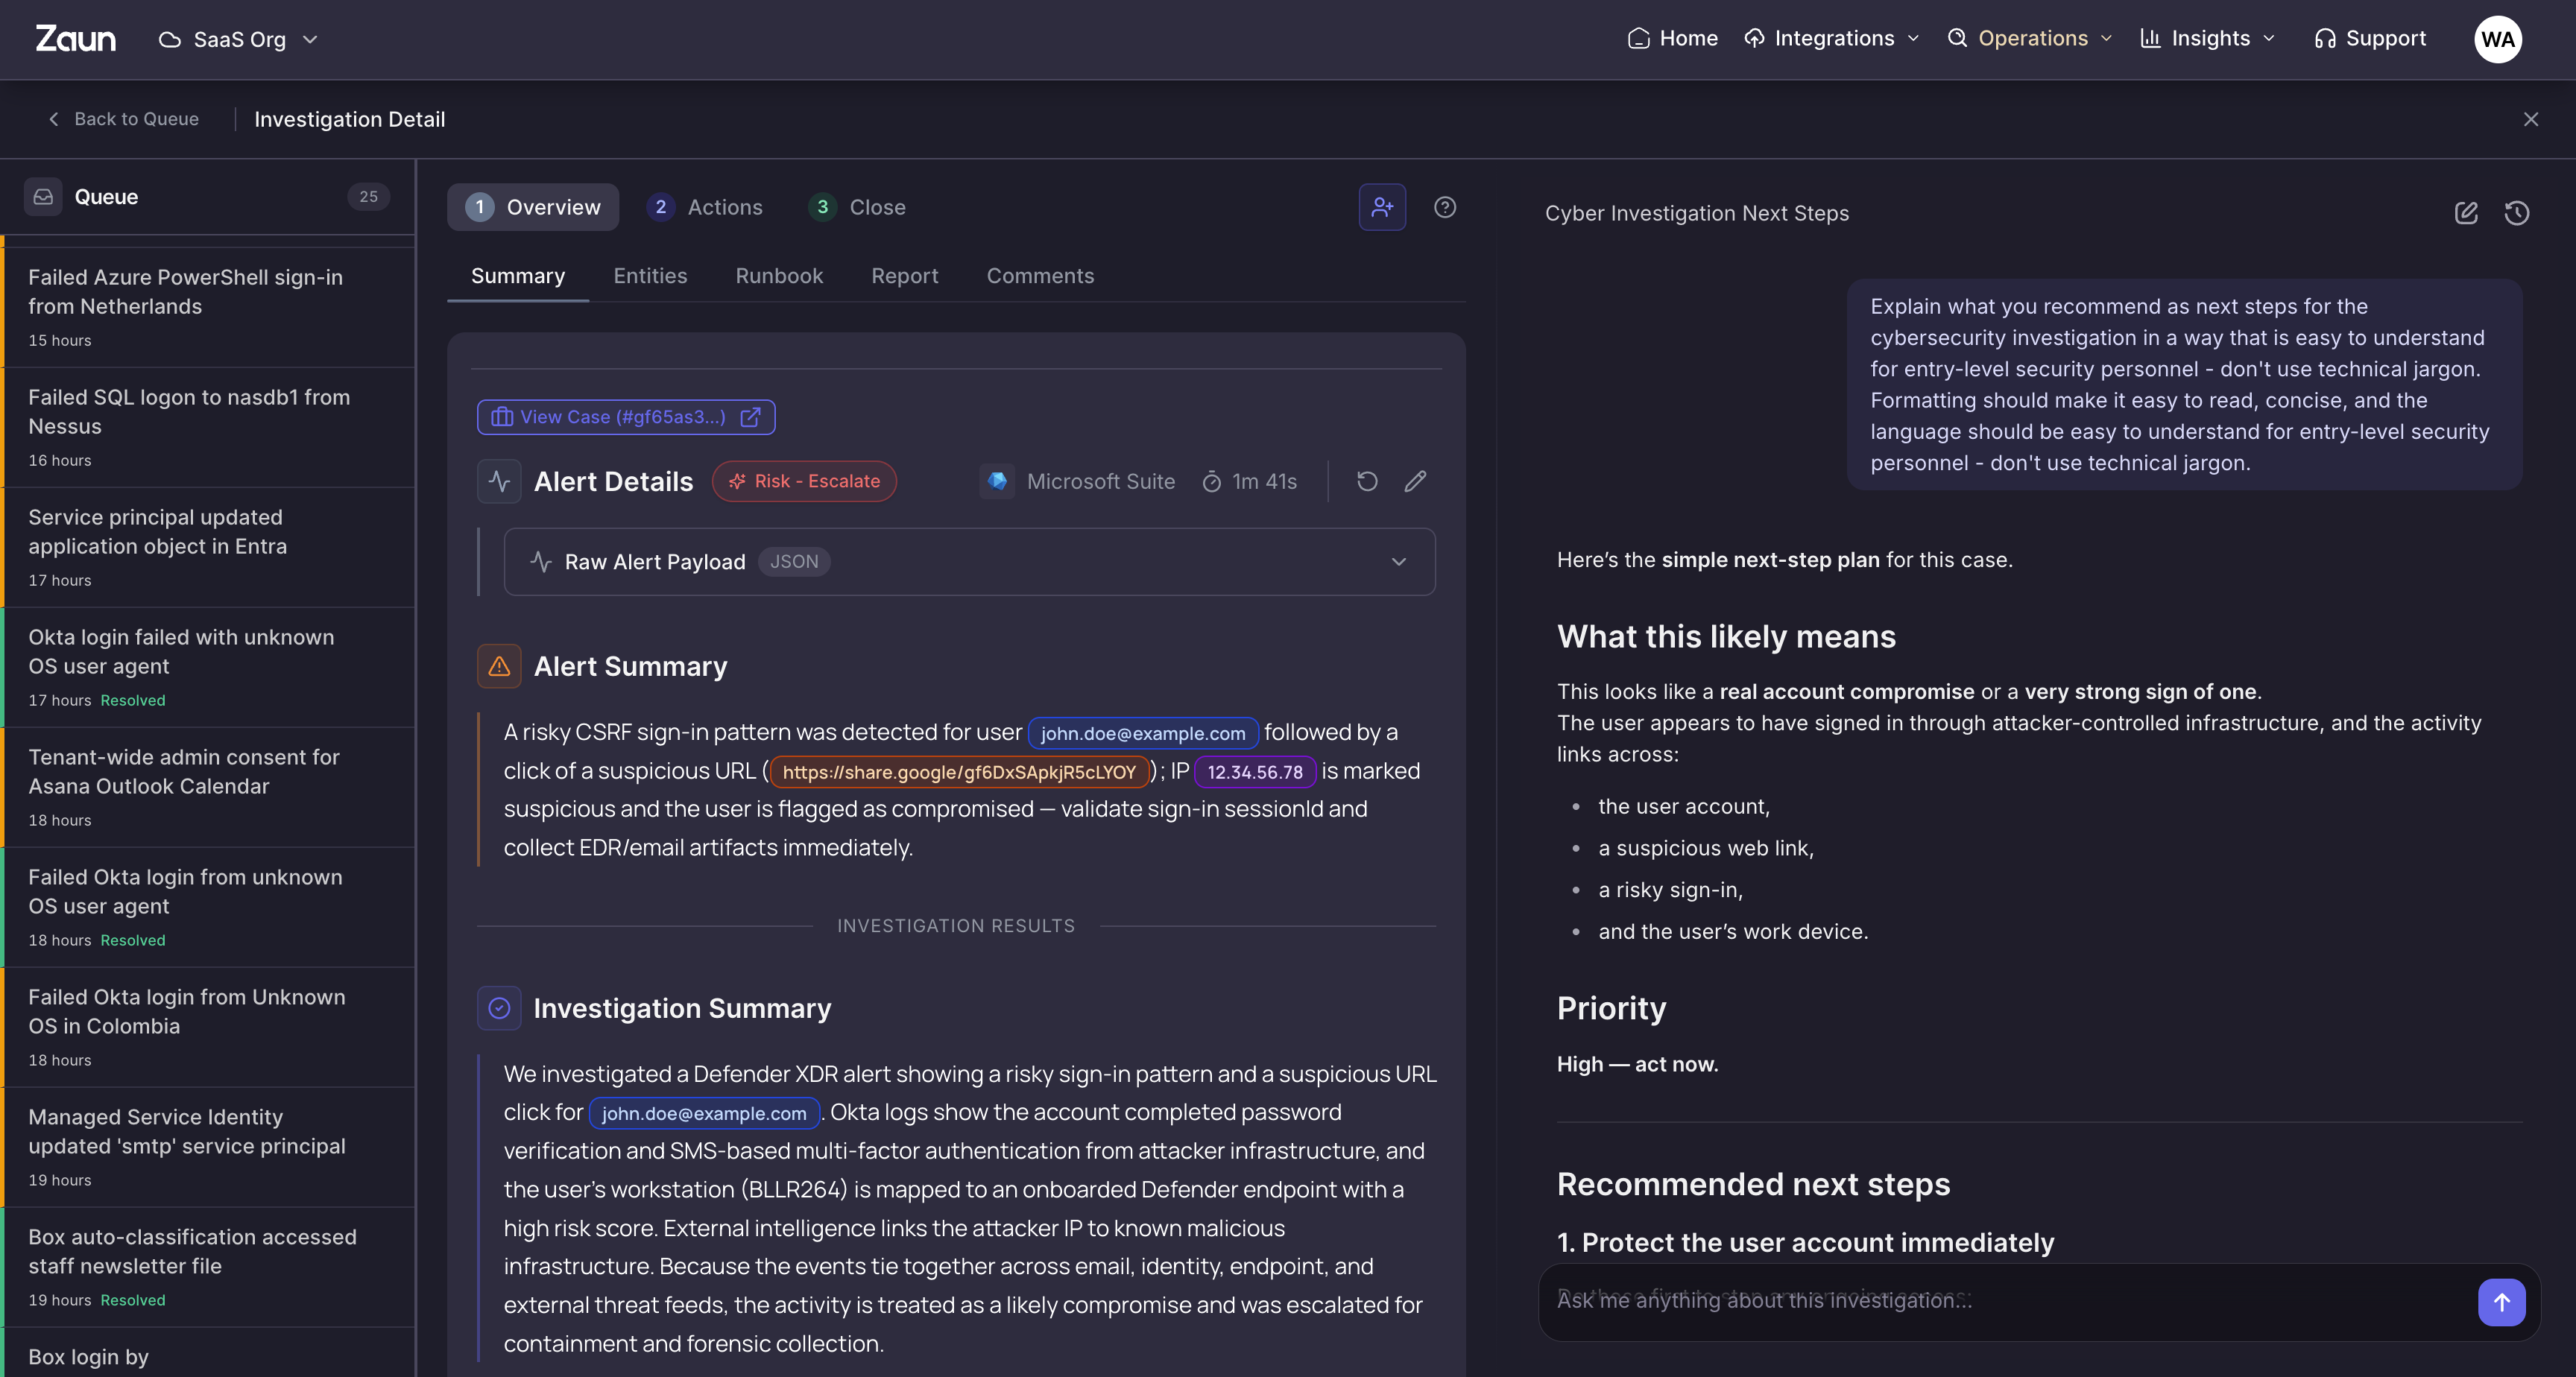
investigation #4271HIGH

OAuth grant from new device on executive account

Auto-summary: actor approved a drive.read grant 14 minutes after a sign-in from an unrecognized device. No matching change ticket. Recommend revoke and rotate.

00:00
detection
oauth_grant.suspicious fired
00:01
collect
pulled actor history (okta, slack, github)
00:03
correlate
matched session anomaly + new device
00:06
verdict
true positive : credential exposure
00:07
runbook
awaiting human approval to revoke
Approve revokeOpen full timeline
evidence graph6 sources · 14 events
324212INV#4271Okta3 events · sign-inSlack2 events · activityGitHub4 events · push eventsAWS2 events · IAMCrowdStrike1 event · EDRGoogle2 events · mail headers
Product view / investigation detail view
Zaun investigation detail with alert summary, raw payload, investigation results, and a Cyber Investigation Next Steps panel with priority and recommended actions

Diagrams and sample records illustrate the workflow. Product views are identified separately; example metrics are not customer results.

Compliance

Continuous compliance, evidence-backed.

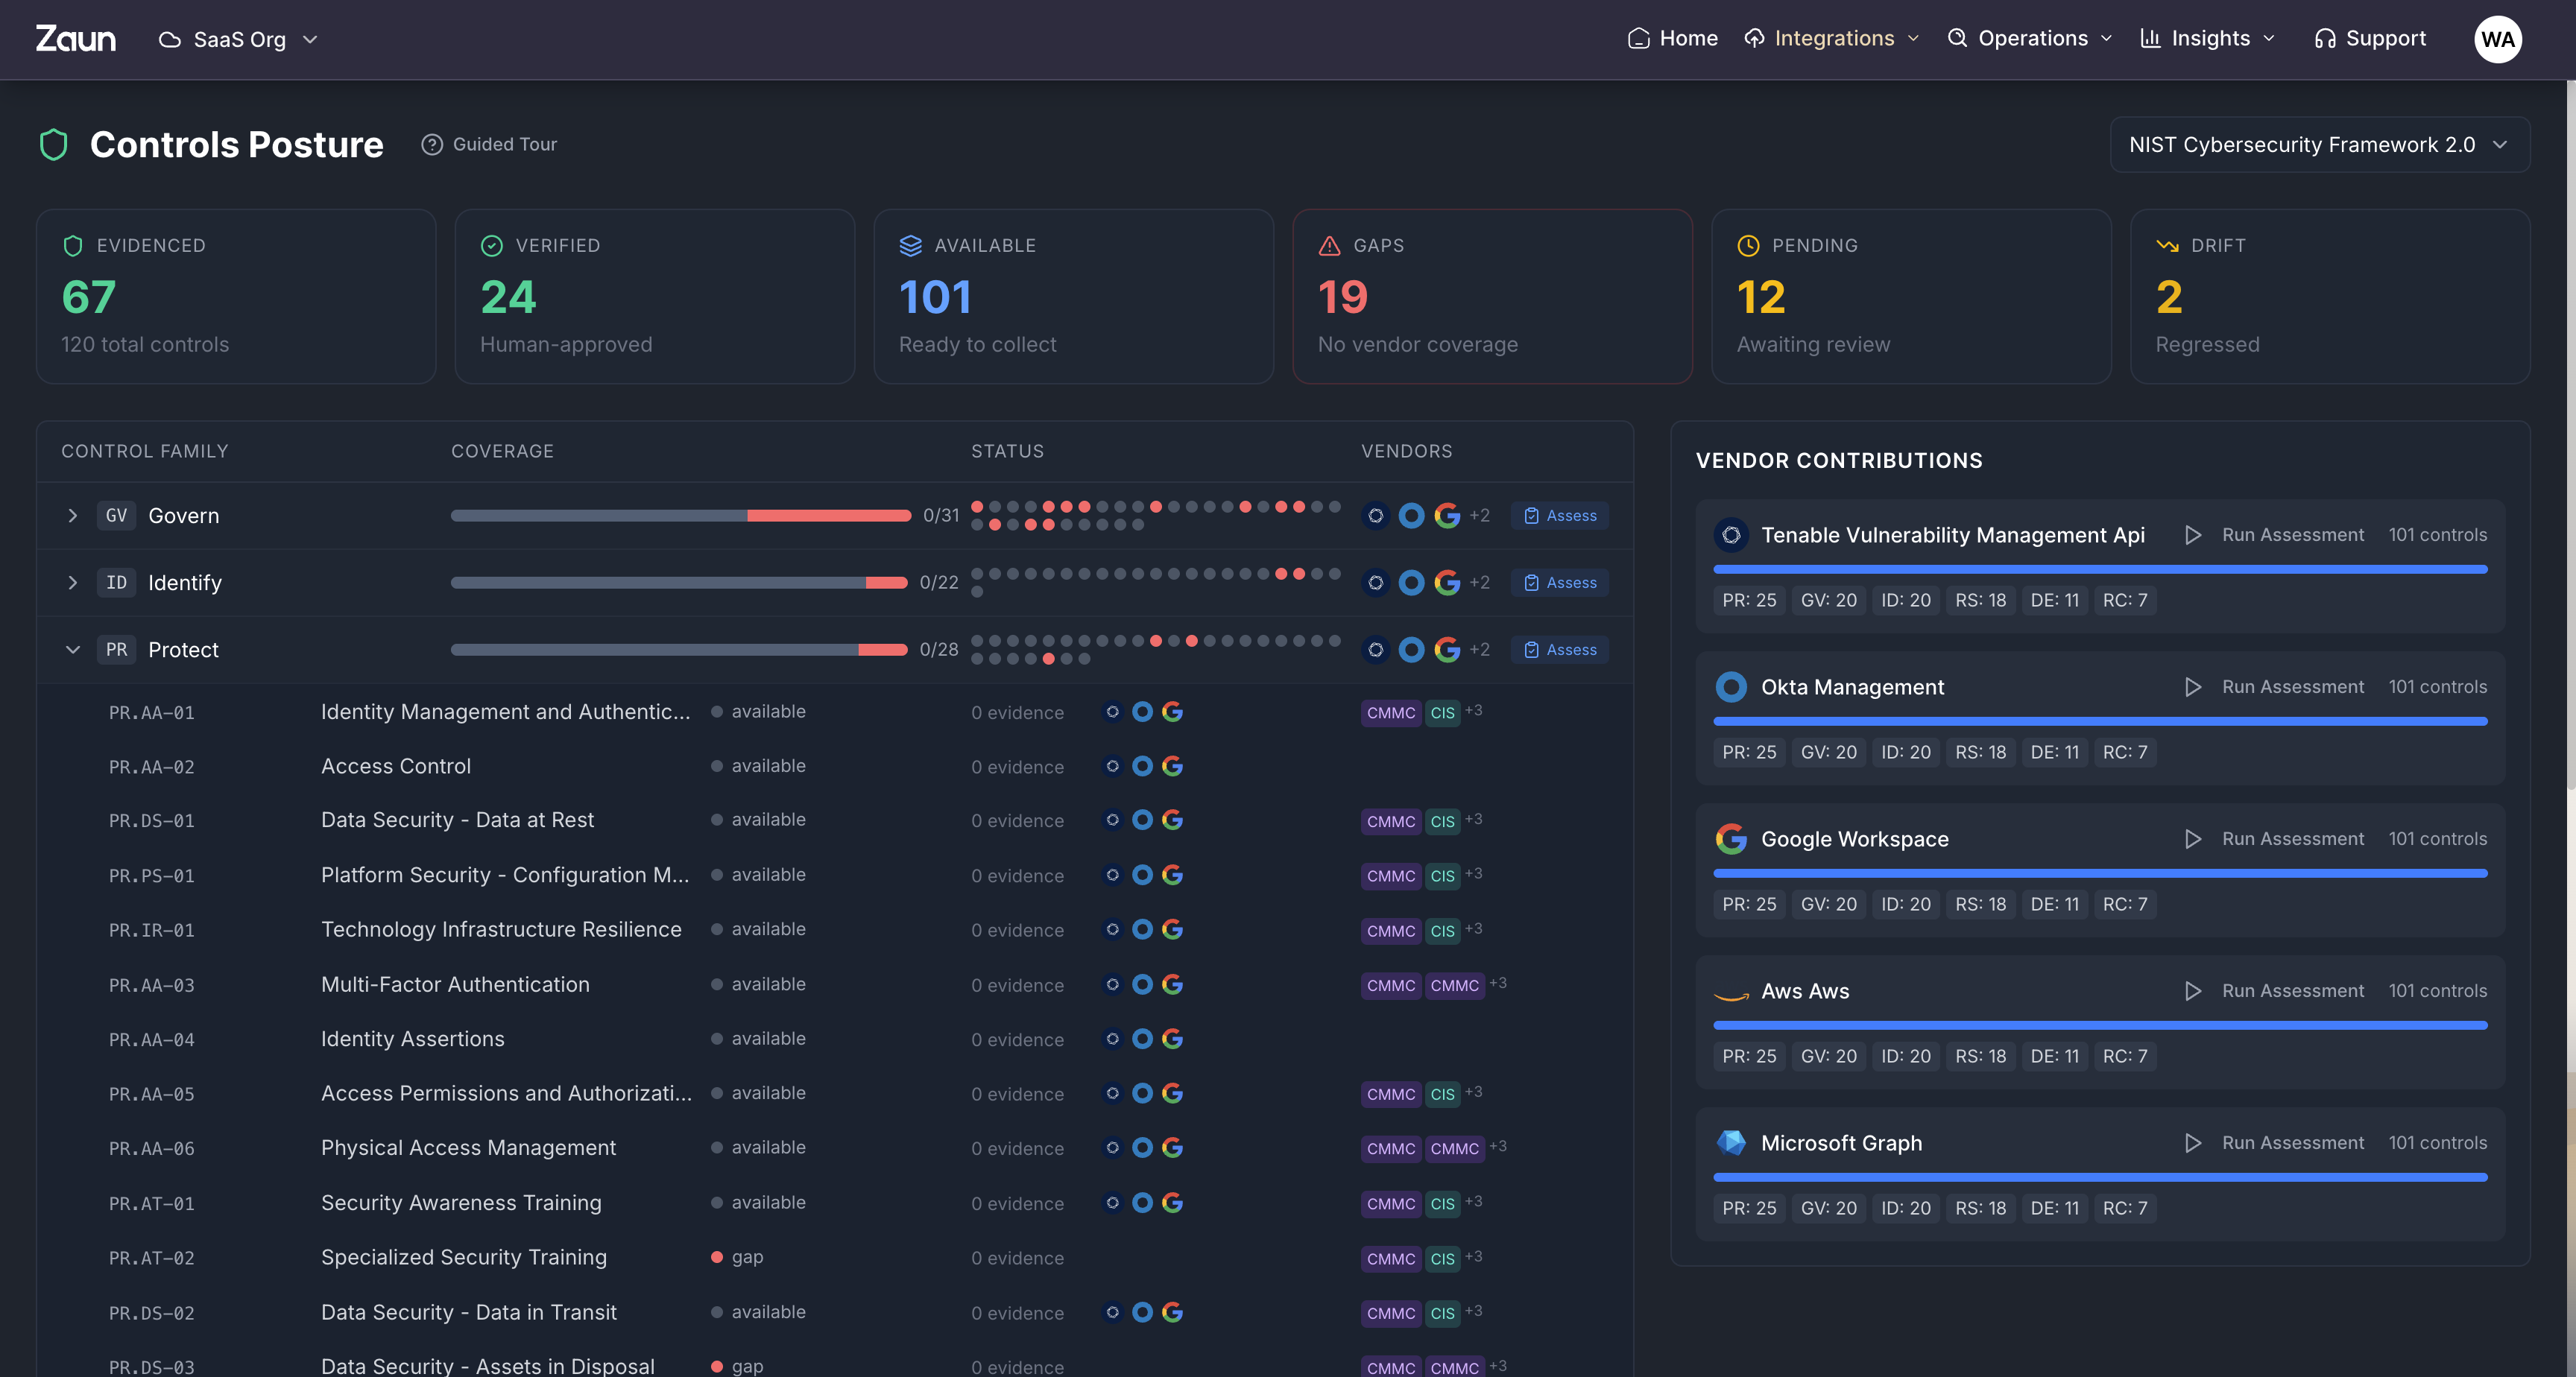
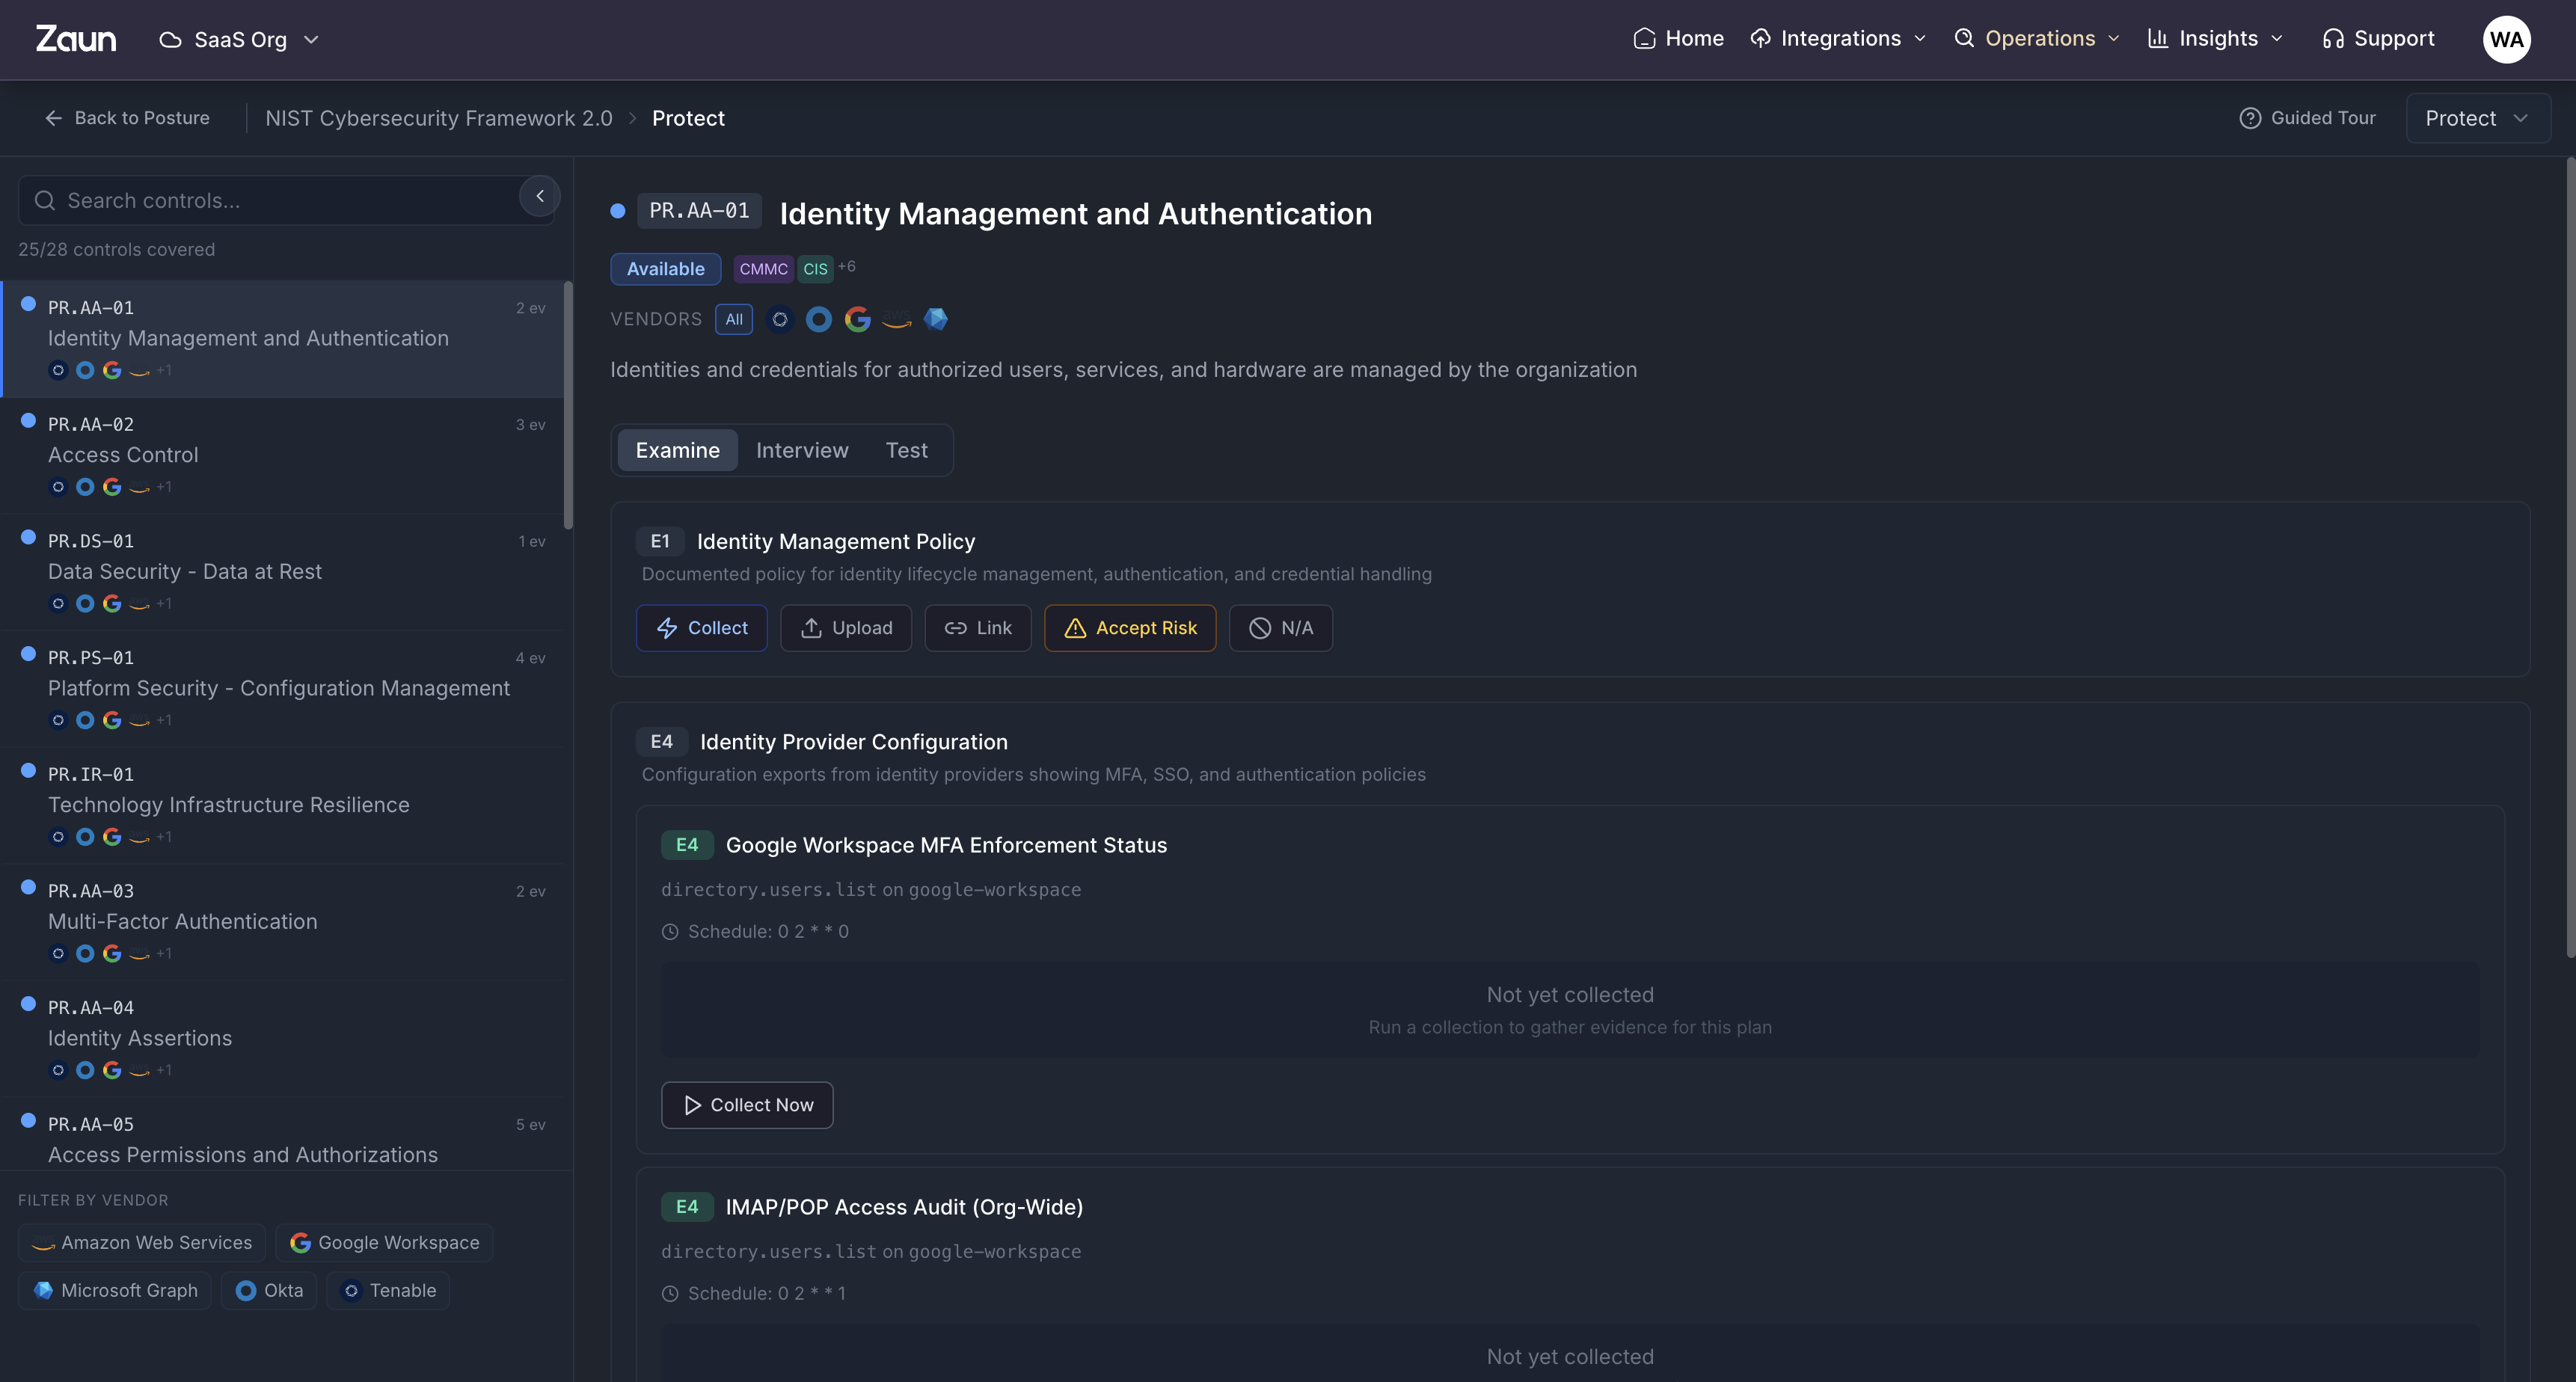
Map relevant controls to available evidence from connected systems. Review gaps, verification status, and supporting records with your team and auditor.
92%
example posture
764
sample control count
SOC 2

SOC 2 Type II

98%
controls156 / 159
audit-ready
ISO

ISO 27001

91%
controls102 / 112
on track
HIPAA

HIPAA

94%
controls48 / 51
audit-ready
PCI

PCI DSS 4.0

87%
controls218 / 251
on track
CIS

CIS Controls v8

96%
controls146 / 153
on track
NIST

NIST CSF 2.0

89%
controls94 / 106
on track
Product view / controls posture
Zaun Controls Posture dashboard for NIST Cybersecurity Framework 2.0 with evidenced, verified, available, gaps, pending, and drift counts plus per-control coverage and vendor contributions
Product view / controls posture
Zaun Controls Posture dashboard for NIST Cybersecurity Framework 2.0 with evidenced, verified, available, gaps, pending, and drift counts plus per-control coverage and vendor contributions

Diagrams and sample records illustrate the workflow. Product views are identified separately; example metrics are not customer results.

Reporting

Reports that make the work clear.

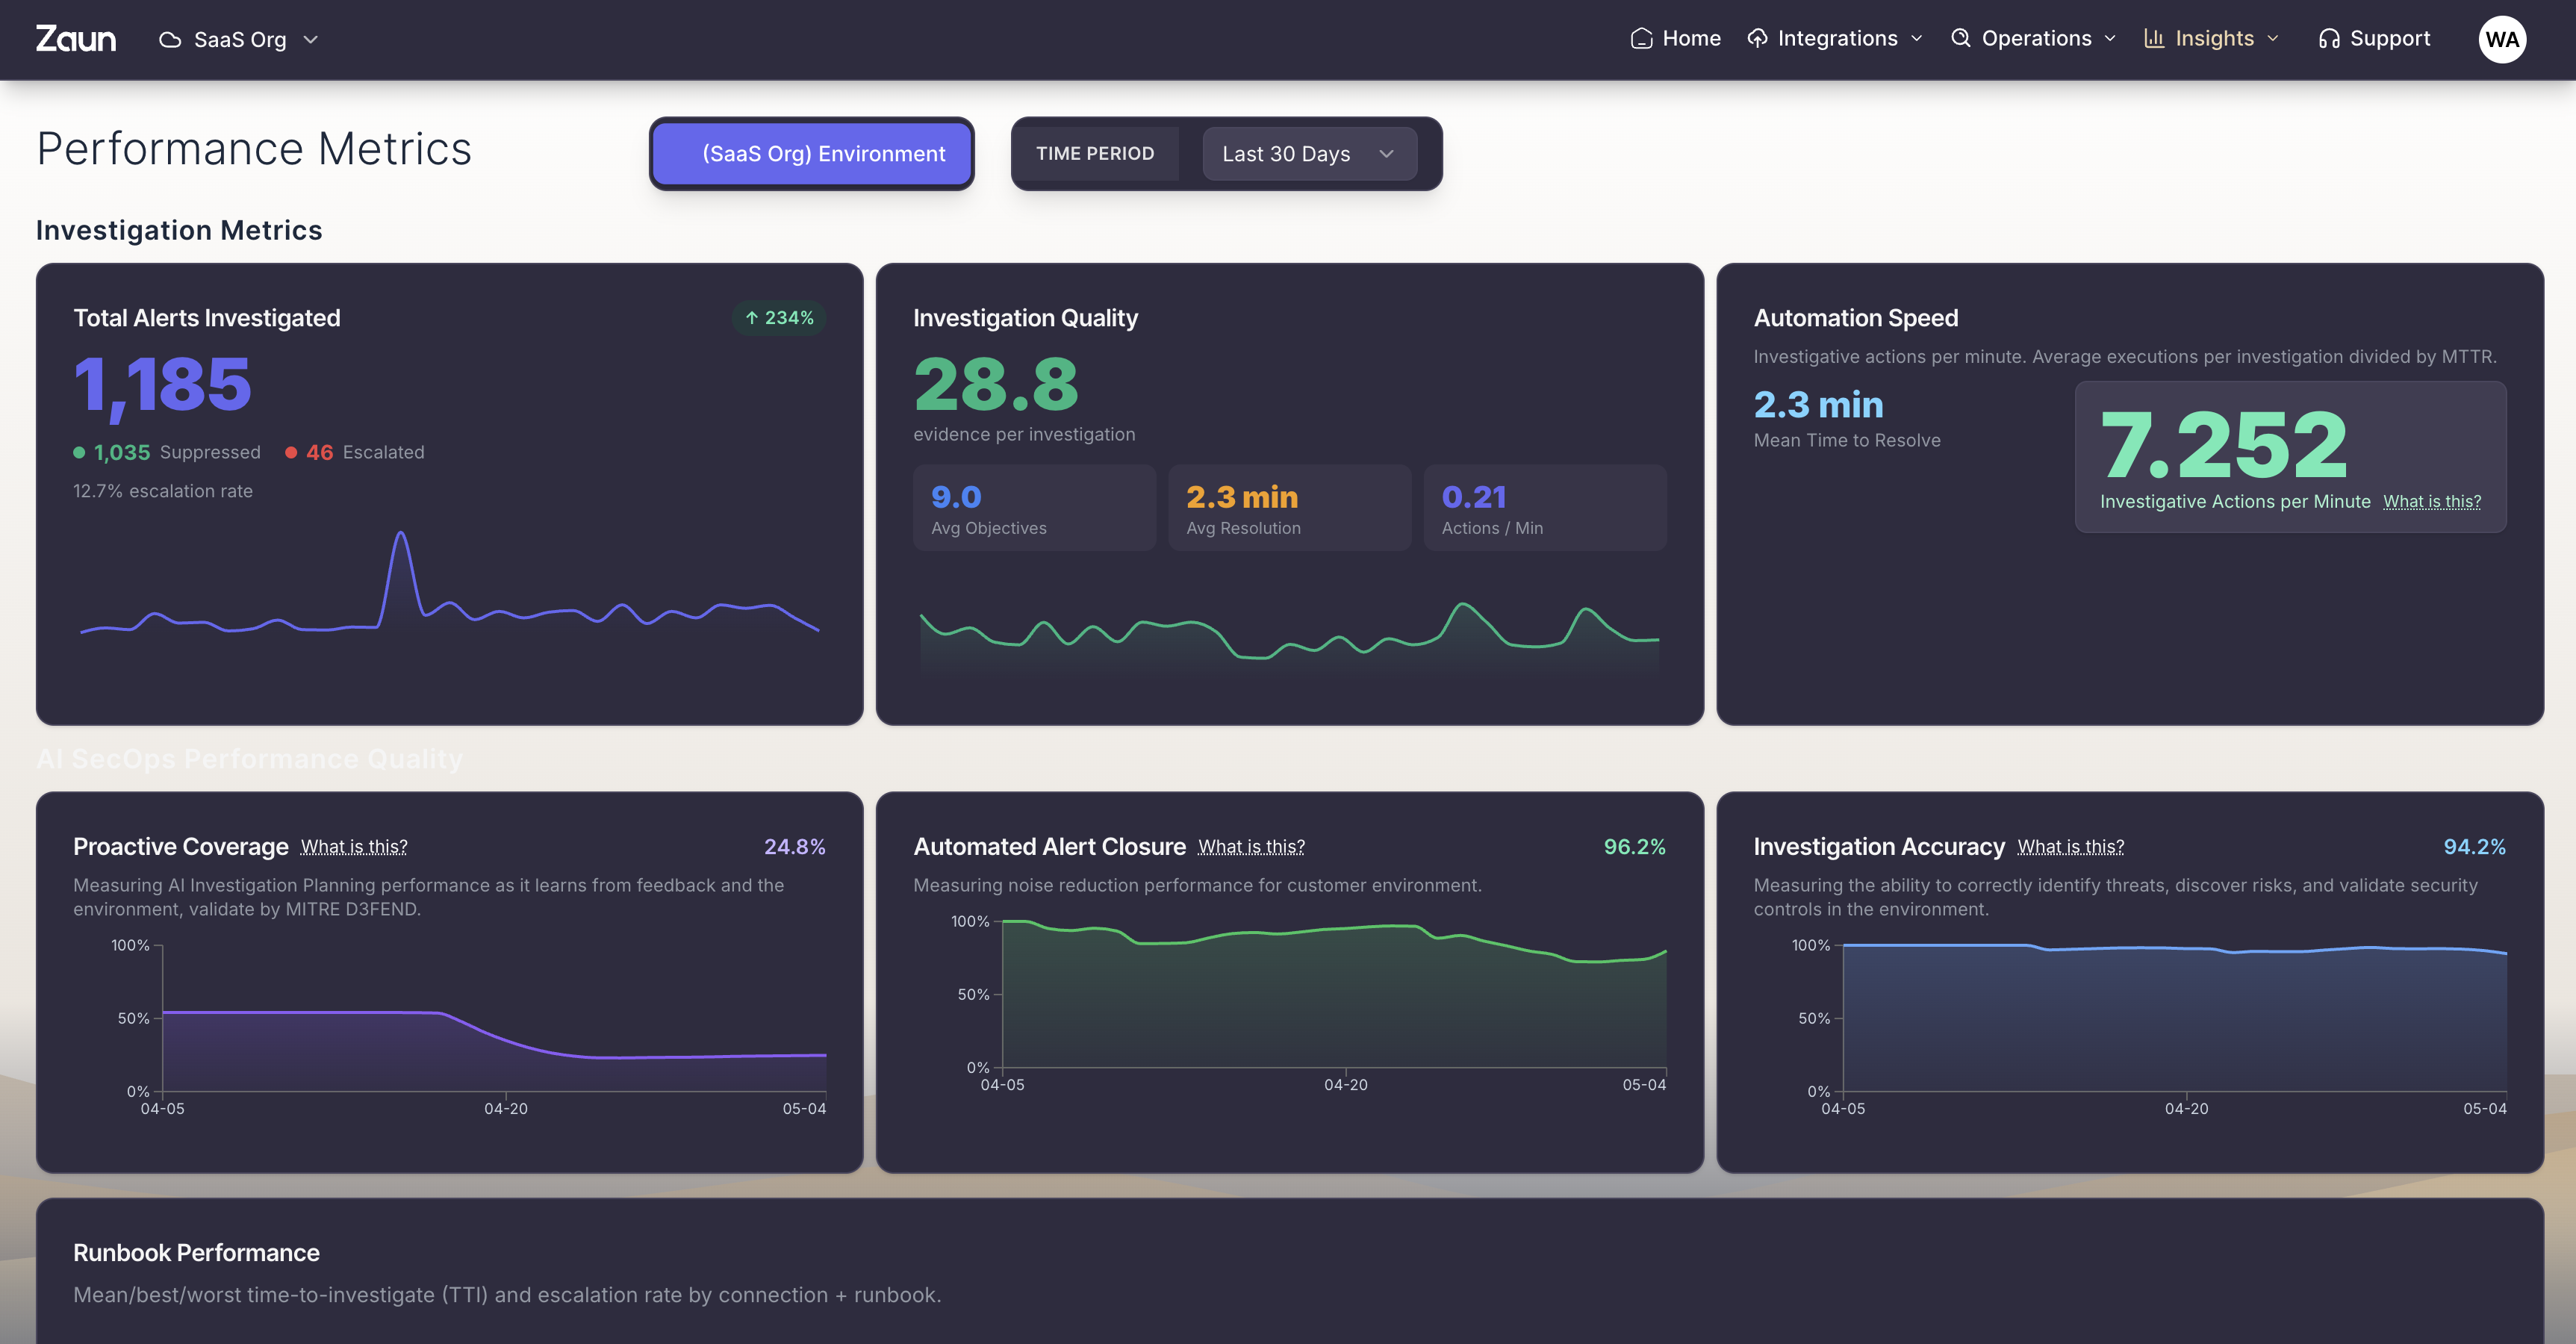
Summarize coverage, posture, response activity, and incidents in plain language. Review the reporting period, sources, and limitations before sharing the result with leadership.

BOARD

Q2 board readout

May 2026 · Executive summary

AUDIT

SOC 2 evidence pack

Continuous controls report

OPS

Weekly coverage

Week 18 · MTTR, incidents, tuning
Coverage trend · 7 weekscoveragemttr (min)
W14
W15
W16
W17
W18
W19
W20
↑ coverage 71 → 96↓ mttr 38m → 14m
Product view / performance metrics
Performance Metrics dashboard with investigation totals, quality, automation speed, proactive coverage, automated alert closure, and investigation accuracy
Product view / performance metrics
Performance Metrics dashboard with investigation totals, quality, automation speed, proactive coverage, automated alert closure, and investigation accuracy

Diagrams and sample records illustrate the workflow. Product views are identified separately; example metrics are not customer results.

Support

An engineer who knows your stack, on call.

Work with a named engineer on your environment, detection priorities, and response workflows. Agree the engagement scope, review cadence, and communication channels with the team.

#zaun-alphacorp5 members · pinned
AK
Asha K.9:14 AM
morning. two platform updates went out overnight: saved-view filters in the lake explorer and bulk runbook export. pinned both in the workspace for you.
MV
Marco V.9:21 AM
also got the new linear integration live. alerts auto-create tickets and the agent threads the verdict back here when it closes.
Y
You9:23 AM
nice. can we refresh the okta detections pack with the new techniques from the v3 release?
AK
Asha K.9:24 AM
already pulled v3.2 yesterday. ~8 new techniques covered, want a quick walkthrough before they go live?
Asha is typing
JY
Johnny Y.
Forward Deployed Engineer
online
CF
Christophe F.
Forward Deployed Engineer
online
TL
Tyler L.
Forward Deployed Engineer
on call
Agreed
response window
24/7
optional 24/7 Human-led Response

Diagrams and sample records illustrate the workflow. Product views are identified separately; example metrics are not customer results.

Pricing

One identity.One price.

Pricing is based on monitored identities. Confirm the scope and terms for your deployment. Ember counts what your auditors count: the staff in your org. Service accounts and AI agents are excluded.

pricing model
Per monitored identity
  • Staff in your organization
  • Service accounts not counted
  • AI agents not counted
Enterprise plan

Add-ons available:

  • 24/7 human SOC response
  • Zaun Intelligent Lake+

Put your security workflow in context.

Review the systems you need to connect, the controls you need to keep, and where Ember can help.